For security vendors, MSSPs, and infosec brands. We earn editorial backlinks on security publications by leading with research, not fear.
Cybersecurity guest posting means publishing technically credible security content on real infosec publications, with a contextual backlink to your brand. The audience here is technical, skeptical, and quick to dismiss anything shallow.
Security marketing has a FUD problem: years of fear-driven pitches trained editors and readers to tune out anything that smells like scare tactics. What earns links is the opposite: precise, honest, technically grounded content that respects the reader's intelligence.
The editorial bar in infosec is the highest in B2B. Writers are practitioners, readers spot errors fast, and publications guard their reputations fiercely. A single technical inaccuracy can end a relationship with an editor permanently.
News cycles create link windows you cannot manufacture. Breaches, vulnerabilities, and regulation changes generate coverage that needs expert commentary within hours. We monitor these cycles and pitch explainers fast. Every target passes our publisher quality screens for real traffic and real editorial standards.
In cybersecurity, research earns links; fear earns indifference.
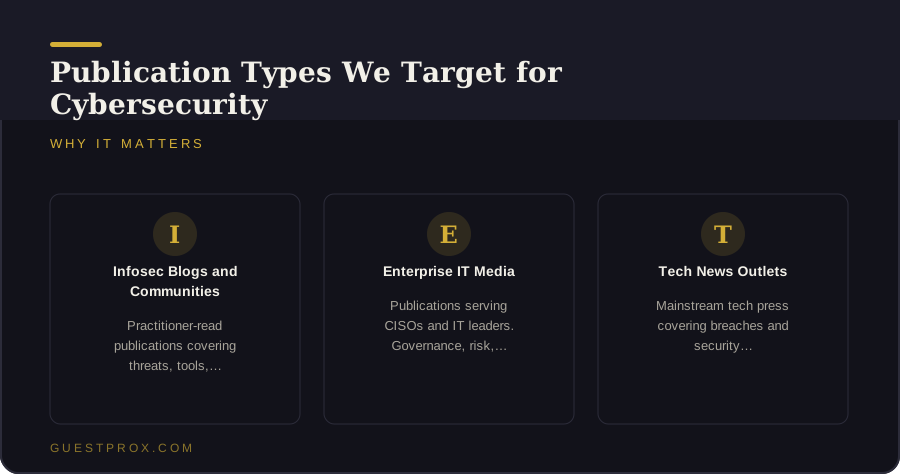
We pitch security publications where technical credibility is the price of entry.
Practitioner-read publications covering threats, tools, and tradecraft. Research-driven content earns links here that the community actually shares.
Publications serving CISOs and IT leaders. Governance, risk, and strategy angles fit their editorial needs.
Mainstream tech press covering breaches and security industry moves. Expert commentary during news cycles earns high-authority citations.
DevSecOps and application security media. Code-level and pipeline-focused content reaches the builders implementing defenses.
Research-grade deliverables, fully reported.
Five steps built for an audience that fact-checks everything.
We study your security segment, the topics gaining traction, and which publications link to competitors. Research gaps become our pitch angles.
We prospect infosec publications with real practitioner audiences and verify traffic. Vendor-blog networks and thin content sites are excluded.
We pitch substance: attack analysis, defense engineering, lessons from incidents. Security editors respond to technical seriousness, not product pitches.
Our writers produce accurate, well-structured security content that respects the reader's expertise. Every claim is grounded; nothing is sensationalized.
Every link is verified live, dofollow, and contextual before reporting with full metrics. Agencies receive white-labeled reports.
Infosec editors are practitioners first. They have configured the tools, read the CVEs, and sat through a thousand vendor pitches. Content that would pass in any other B2B niche gets rejected here for lacking technical depth or, worse, for getting a detail wrong.
Fear-based content fails twice: editors reject it and readers distrust it. The industry spent a decade crying wolf, and the audience learned. What works is calm, precise analysis: what happened, what it means technically, what practitioners should actually do.
Vendor neutrality matters. Security publications will not run content that is a product pitch wearing an educational costume. We write genuinely useful analysis where the brand's expertise shows through the quality of thinking, not through mentions. A competitor link-gap check in this niche usually reveals that rivals are buying mentions while the editorial opportunities sit untouched.
Incident analysis with technical depth is the premium format. Not hot takes within an hour of a breach, but the careful breakdown a day later: attack vectors, what the logs would show, what defenders should check. Editors need this and cannot produce it without practitioner input.
Original research earns links at a scale nothing else matches. Survey data from your customers, anonymized incident statistics, analysis of your own telemetry: numbers no one else has are pitchable to every tier of security media.
Practitioner guides with real commands, configurations, and decision frameworks get bookmarked and cited for years. We work with your technical team to extract the knowledge, then shape it for publication. For the full method, see our campaign process.
Security link sellers prey on marketing teams without technical staff. They offer placements on sites with security branding and content that falls apart under expert review. Your buyers are practitioners; a link from a site they do not respect can actively harm credibility.
The CVE-chasing content farm is the specific trap. Sites pumping out shallow vulnerability summaries to rank for trending CVEs, selling links in every article. No real readership, no editorial standards, just trend-chasing content built for link buyers.
Demand technical review of every target. If your own security team would not cite the publication, neither should your link profile. Our publisher standards verify real traffic, real authorship, and real editorial process before any outreach begins.
Marketing teams without technical reviewers are the most exposed buyers in this niche. If no one on your side can evaluate whether a placement is technically credible, you are trusting the vendor completely. Insist on reviewing target sites yourself, and have your technical team spot-check the content. A vendor who resists technical scrutiny is telling you exactly what you need to know. Technical scrutiny is not optional in this niche. Make it a contractual requirement: your team reviews every target site and every draft before publication. Legitimate agencies build this into their process without being asked. In security, trust is the product, so protect it fiercely. Verify first, publish second, rank third.
Tell us about your security offering. We will map editorial placements on publications practitioners trust.
Chat on WhatsApp →Cybersecurity overlaps with technology, software, and editorial PR.
Authoritative sources if you want to go deeper on this topic.
Because the industry has been saturated with it for a decade. Editors and readers alike have developed strong filters against scare tactics, and practitioners publicly criticize vendors who use them. Research, honest analysis, and practical defense guidance earn editorial space; FUD earns deletion.
Link sellers in this space operate thin vendor-blog networks with no practitioner audience. We do manual outreach to genuine security publications and earn placements with content that survives expert review. Every site is traffic-verified first. No PBNs, no schemes, 100% white hat.
We research deeply before writing: your documentation, public research, threat reports, and the publication's own standards. For highly specialized topics we work from your team's input and shape it into editorial-grade content. If a topic exceeds what we can cover credibly, we will say so rather than fake it.
We don't publish prices. Every campaign is scoped to your segment and targets, so message us on WhatsApp at +1 (213) 582-6001 for an exact number.
Yes. Since 2018 we have delivered 1259+ guest posts with deep white-label experience. Your clients see your brand on every report, your pricing stays yours, and GuestProx never appears in deliverables.
For specialized topics, yes, and we make it painless. We work from your documentation, threat research, and a short briefing call, then shape it into editorial-grade content. If a topic exceeds what we can cover credibly, we will say so rather than fake expertise your audience would expose.
Tell us about your security brand. We will map the editorial placements that respect your audience's intelligence.
Global Service Delivery